Endpoint Hardening: CISA and CIS Priorities for a 30–90 Day Rollout
Build an endpoint hardening checklist from CISA and CIS guidance, prioritize urgent controls, and plan a 30 to 90 day rollout with managed services.
Read more
Tips, trends, and insights on managed IT, cybersecurity, copiers, and the technology that runs your business.
Build an endpoint hardening checklist from CISA and CIS guidance, prioritize urgent controls, and plan a 30 to 90 day rollout with managed services.
Read more
See how Azure Cost Management helps FinOps teams track spend, set budgets, and act on alerts, with a quickstart of 8 steps and managed…
Read more
CMMC Phase II is paused, but defense contractors still face DFARS and NIST duties. Check assessment scope, update SPRS, and submit annual affirmations.
Read more
See how security teams spot MFA fatigue attacks, use number matching as a bridge, track sign ins with telemetry, and plan MFA that resists…
Read more
SMB action plan for immutable backups: set retention, keep an offline copy, and run 2–3 restore drills on one workload. Managed IT help available.
Read more
Compliance first IT asset disposal: NIST aligned sanitization, chain of custody records, certified recyclers, or managed services for SMBs.
Read more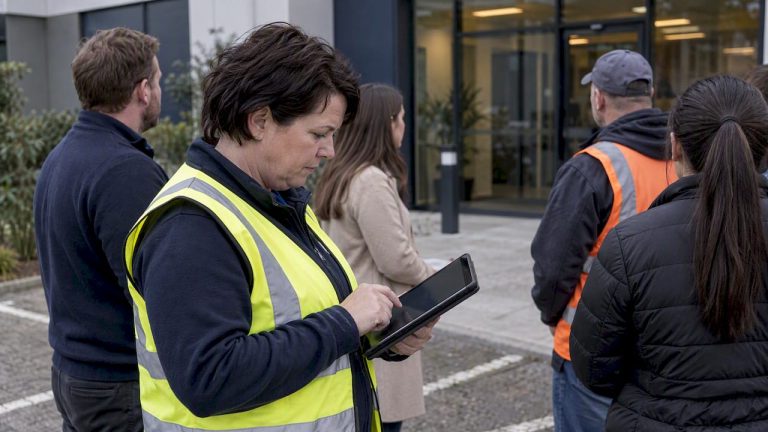
For IT and facilities teams, compliance first visitor management systems that secure mustering, minimize PII, and use a seven step rollout.
Read more
A practical playbook for people and SMBs to prevent account takeover using phishing resistant MFA like passkeys, unique long passwords, and regular app...
Read more
Cloud access control for facility managers: prioritize IdP/HR sync, OSDP readers, local first validation, and clear migration terms.
Read more
Practical, risk tiered remote access policy for IT admins with testable clauses, device tier rules, and a 30–90 day rollout plan plus Mavericks...
Read moreGet a free assessment and see how Mavericks can simplify your technology.